RBAC for SaaS: Insights from Managing Nine User Roles
Discover practical lessons in RBAC for SaaS including multi-tenant authorization and managing role-based dashboards from a platform with nine distinct roles.
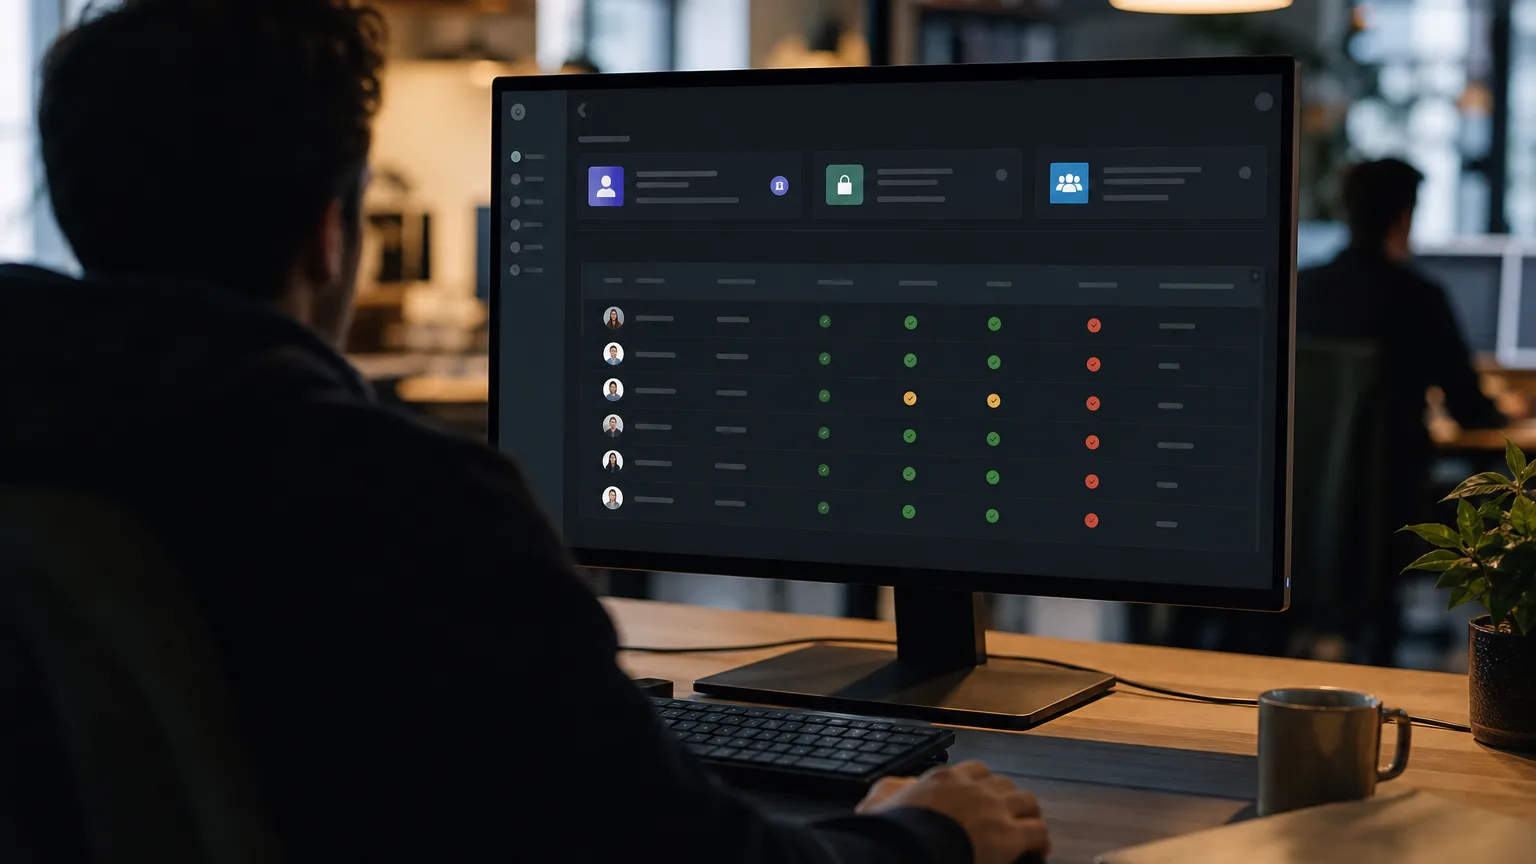
Key takeaways
- RBAC is essential for managing permissions in complex multi-tenant SaaS platforms effectively.
- Defining user roles with clear boundaries simplifies dashboard design and enhances security.
- Multi-tenant authorization requires isolating data access per tenant and role to prevent leaks.
- Proper RBAC implementation reduces maintenance overhead and improves user experience.
- Communication with stakeholders is crucial to align role capabilities with business needs.
What is RBAC and why is it critical for SaaS platforms?
Role-Based Access Control (RBAC) is a framework that restricts system access to users based on their assigned roles. For SaaS platforms — especially multi-tenant ones — RBAC is key to secure, scalable authorization. Roles define what functionality and data a user can access in their tenant and across the system.
Efficient RBAC leads to clear separation of duties, reduces risks of unauthorized access, and enables smoother feature releases targeted by role. For a deep dive on SaaS design considerations, see How Much Does It Cost to Build a SaaS MVP in 2026?.
What challenges does RBAC face in multi-tenant SaaS?
Multi-tenant SaaS systems serve multiple clients (tenants) with isolated data while running on a shared platform. This setup complicates RBAC due to:
- Tenant data isolation: Users must only access their own tenant’s data.
- Role granularity: Different tenants might require different permissions for similar roles.
- Shared resources: Some features may be cross-tenant but restricted by role.
Implementing multi-tenant authorization means designing permissions both at the tenant level and role level. You must ensure every query and action guards against unauthorized access across both dimensions.
How to design roles in a SaaS with multiple distinct user types?
From working on complex platforms with up to nine roles, a structured approach helps:
- Identify core user roles: e.g., Super Admin, Tenant Admin, Manager, Editor, Viewer.
- Define clear boundaries: Specify capabilities and feature access meticulously per role.
- Plan for role overlap: Some roles might share permissions partially.
- Account for future roles: Leave room to add roles without breaking existing rules.
This approach simplifies authorization logic and clarifies what each role’s dashboard should display.
What does role-based dashboards entail?
Dashboards tailored to roles improve user experience by showing relevant data and actions only. For example:
- A Super Admin sees platform-wide analytics and user management.
- Tenant Admins manage users and billing within their domain.
- Editors focus on content creation tools.
- Viewers access read-only reports.
Designing dashboards with role context avoids overwhelming users and reduces potential errors or unauthorized actions.
Lessons learnt from managing nine roles in a SaaS platform
- Consistent permission checks: Always verify role and tenant context in every API endpoint or UI action.
- Use central RBAC management: Maintaining a single source for role definitions prevents drift.
- Testing is non-negotiable: Automated tests for role permissions help catch regressions early.
- Performance considerations: Efficiently cache permissions where possible to reduce overhead.
- User feedback matters: Users can highlight confusing role overlaps or missing permissions.
Experience shows skipping or underestimating these steps leads to security gaps and costly refactoring.
Tools and Frameworks for Implementing RBAC in SaaS
You have different options depending on stack and complexity:
| Approach | Description | Trade-offs |
|---|---|---|
| Framework built-ins | Laravel’s Gate/Policies, NextAuth.js with middleware | Easy to implement, less flexible at scale |
| External Authorization | OPA (Open Policy Agent), CASL, or Auth0 RBAC | Better scalability, complexity, cost |
| Custom RBAC layer | Tailored solution storing roles/permissions in DB | Maximum flexibility, higher dev effort |
For Laravel apps, features like Filament integrate well with RBAC. For React/Next.js, libraries like CASL or NextAuth help enforce rules on front- and back-end.
Practical improvements beyond permissions
RBAC intersects with other areas, worth considering:
- Audit logging: Track role-based actions for compliance.
- Role hierarchy: Sometimes roles inherit permissions, reducing duplication.
- Self-service user management: Tenant admins can assign roles within their scope.
These add robustness and usability to your SaaS platform.
Summary
Role-based access control is foundational for secure, maintainable SaaS platforms with multiple tenants and user types. Designing precise roles and role-based dashboards, enforcing multi-tenant authorization rigorously, and using proper tools prevents security issues and improves UX. Planning for scale with consistent policies and automated tests protects against costly future changes.
For a practical reference to managing roles and a rich admin interface, take a look at the NetWay Solutions case study.
A practical lesson from experience
One mistake I avoid is skipping early alignment on roles and permissions with stakeholders. Clarifying who should do what upfront saves countless iterations of fixing wrong access and redesigning dashboards. RBAC is not just a technical feature; it’s a business process enabler.
If you want expert help building SaaS platforms with thoughtful multi-tenant authorization and well-designed role-based dashboards, see my dedicated service and get in touch: SaaS & web app development and contact me.
Related resources
- Laravel vs Next.js: Which Framework for Your Web App Stack? — compare core frameworks for backend and frontend roles
- Launching an Online Store: Payment, Delivery & Hosting — considerations of access control in e-commerce
- Blog category on SaaS development — broader insights for SaaS builders
FAQs
What is the difference between RBAC and ABAC?
RBAC restricts access based on predefined roles, while Attribute-Based Access Control (ABAC) uses more granular rules involving user, resource, and environmental attributes for decisions. RBAC tends to be simpler to implement.
How do SaaS platforms ensure tenant data isolation?
They combine role checks with tenant context, ensuring queries and actions are filtered by tenant ID. This prevents users from accessing other tenants’ data.
Can a user have multiple roles in RBAC?
Yes, many systems support assigning multiple roles per user, which aggregate cumulative permissions. This requires careful conflict management.
How can you test RBAC rules effectively?
Automated tests should cover positive and negative cases for each role accessing each sensitive feature or data type. Integration and end-to-end tests catch interface issues.
Are there common RBAC mistakes to avoid?
Common errors include overly broad roles, hardcoding permissions, inconsistent enforcement, and neglecting to update roles as the product evolves.
What is a role-based dashboard?
It is a user interface that displays information and actions tailored to a user's role, improving usability and security by hiding irrelevant or unauthorized options.
Frequently asked questions
What is the basic purpose of RBAC in SaaS?
RBAC controls access by assigning users specific roles that determine their permissions, ensuring security and proper functionality segmentation in SaaS.
How does multi-tenant authorization differ from standard RBAC?
Multi-tenant authorization adds a layer where permissions must be enforced not only by roles but also restrict data and actions to the user’s own tenant.
Can RBAC prevent security breaches in SaaS?
While RBAC strengthens security by limiting access, it must be correctly implemented and regularly reviewed to effectively prevent breaches.
Is RBAC suitable for all SaaS applications?
RBAC works well for most SaaS, especially those with multiple user types and tenants, but simpler apps might use basic access controls instead.
What tools help manage RBAC in React and Laravel projects?
Laravel offers native policies and packages like Filament; React projects commonly use libraries such as CASL and NextAuth for RBAC management.
- #rbac
- #saas
- #multi-tenant
- #authorization
- #dashboard
- #security
Written by
Zubayer al Hasan is a full-stack developer and designer who builds SaaS platforms, e-commerce stores and admin tools with Laravel, React and Next.js for clients worldwide. He is based in Dhaka, Bangladesh, and works remotely across time zones.
Keep reading
SaaS development
Laravel vs Next.js: Which Framework for Your Web App Stack?
Choosing between Laravel and Next.js depends on your project requirements, team skills, and long-term priorities.
4 min read
SaaS development
How Much Does It Cost to Build a SaaS MVP in 2026?
Understand the cost factors for building a SaaS MVP in 2026 and how to hire developers effectively worldwide.
4 min read
E-commerce
Launching an Online Store: Payment, Delivery & Hosting
Explore key decisions on payment gateways, delivery methods, and hosting for launching your online store successfully.
4 min read